

A recent wave of cyberattacks targeting South Korea’s financial sector may have been carried out with the help of artificial intelligence tools, according to cybersecurity firm CrowdStrike.
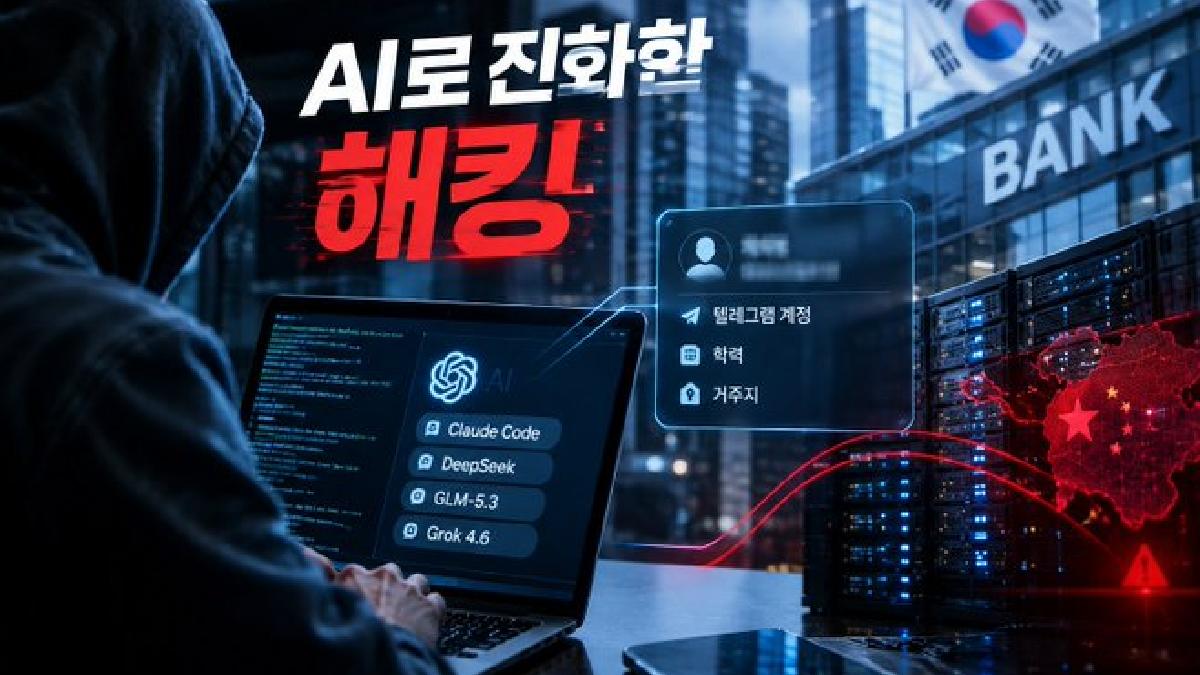
The company said the suspected attacker might be a 26-year-old person based in China’s Guangdong province, although the individual’s identity has not been confirmed.
CrowdStrike said the attacks took place between late September and early October and involved several South Korean financial institutions.
The campaign targeted systems related to financial services like loan inquiry service for financial brokers and a mobile work-support system of staff employees. There were also reports of breaches in the banks Hana Bank, KB Kookmin Bank and Shinhan Bank.
What’s so special about this case is that AI tools were used in the attacks. In a statement, CrowdStrike said the threat actor used ARTEX, an open-source agentic penetration testing tool developed in China and large language models.
Claude Code sessions, ARTEX configuration files and other materials provided evidence of how the suspected attacker operated.
According to CrowdStrike, ARTEX appeared to use DeepSeek v4.1-Flash as its main AI model. GLM-5.3 and Grok 4.6 were also used in the Claude Code sessions.
The research has provided insights on how AI systems could automate or speed up parts of cyberattacks, which could be a challenge for banks and other organizations trying to cope with increasingly complex digital networks.
There was also an unusual clue in the attacker’s interactions with Claude Code, investigators found. The user asked the AI tool to prepare a security researcher resume describing penetration-testing experience in one session.
Personal information included age, education, location and a Telegram profile. CrowdStrike said the user’s details may point to a person in Guangdong but said that the evidence does not prove that the suspect’s identity.
The activity also offered some clues about the motive. CrowdStrike said the attacker asked Claude about marketplaces where stolen South Korean data could be sold and about Korean-language Telegram groups involved in data trading.
Based on the evidence, the cybersecurity firm had moderate confidence that the actor was likely Chinese-speaking and financially motivated.
The campaign was said to have been based on multiple servers and proxy connections. CrowdStrike identified a Hong Kong server that appeared to be the main attacker-controlled infrastructure while another server hosted the ARTEX installation that was used in the attacks on South Korean financial institutions.
The case is only the latest example of international concern with the use of AI in cybercrime. As AI agents become better at coding, research and automation, cybersecurity experts are increasingly concerned that criminals can harness those skills to speed up attacks.
The South Korean authorities are investigating the breaches, but the extent of the stolen information and the identity of the attacker are unclear. CrowdStrike has not attributed the activity to a named threat group.