

Google has just released a security update for Pixel smartphones after identifying a serious vulnerability in the devices’ cellular modem that may have been exploited in limited, targeted attacks.
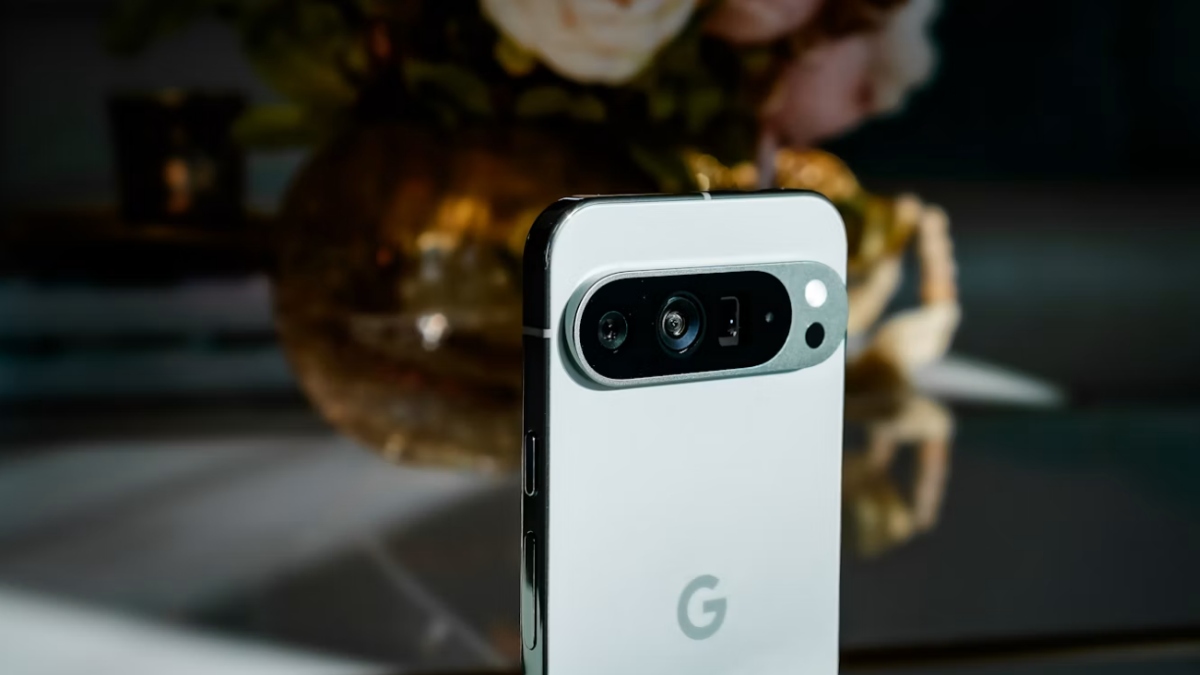
The vulnerability, which is marked as CVE-2026-58704, affects the cellular modem component and could allow an attacker to bypass permission checks and escalate privileges. Google has said it may be exploited in specific attacks.
The disclosure has attracted renewed attention from security researchers because the vulnerability can apparently be exploited without any interaction from the phone owner. Such attacks are called “zero-click” attacks, but the exact techniques used by the attackers have not been publicly disclosed.
Pixel Modem Vulnerability Could Enable Privilege Escalation
CVE-2026-58704 is a security flaw in the cellular modem of supported Pixel devices. Google's September 2026 Pixel security bulletin says it believes that the vulnerability is under some limited, targeted exploitation.
The vulnerability is a permission bypass caused by a logic error in the modem software. The security researchers say that, if exploited, the flaw can allow an attacker to move beyond the modem's normal security limits and gain more privileges on the device.
This is particularly significant because there is no user interaction for exploitation. In a zero-click attack, a victim does not need to click on a malicious link, download a file, or open an attachment to trigger the vulnerability.
However, the information available from Google does not indicate that all Pixel users are at imminent risk or that attackers can automatically take control of every affected device. Google has described the exploitation as limited and targeted.
It has also not identified the attackers or explained who is being targeted. Details about these attacks remain limited.
Google Releases September Pixel Security Update
Google has addressed the vulnerability as part of its September 2026 Pixel security update. The Pixel Update Bulletin states that devices running security patch level 2026-09-05 or later receive the fixes covered by the bulletin. Google has encouraged customers to accept the latest updates.
The CVE-2026-58704 fix is part of a bigger security update. Google addressed 110 vulnerabilities for Pixel devices in the September release, security researchers reviewing the bulletin say. The fixes include privilege escalation, information disclosure, remote code execution, and denial of service.
The wider September Android security bulletin also contains fixes for several vulnerabilities across Android components. Google said devices with the September 5 security patch level or newer address the relevant issues covered by the bulletin.
The Pixel update also arrives alongside Google's September Pixel software release, which includes other functional improvements as well as security improvements.
What Pixel Users Should Do
Pixel owners should check whether their phones have received the September 2026 security update and install it if available.
A user can check for updates in the Settings menu under the software or security update section of the device. The point is to check if the device has a security patch level of September 5, 2026, or later, as set out in the Google Pixel security bulletin.
The warning is especially important because CVE-2026-58704 is not just a theoretical vulnerability. Google has acknowledged the possibility of limited, targeted exploitation, while the US Cybersecurity and Infrastructure Security Agency (CISA) has added the vulnerability to its Known Exploited Vulnerabilities catalogue.
At the same time, there is no public evidence that the vulnerability has been used in a broad attack against ordinary Pixel users. Google's description points specifically to limited and targeted exploitation.
The incident shows why security updates are important even if a vulnerability doesn’t lead to a huge attack. Modem-related flaws are particularly relevant since cellular connectivity is a fundamental part of modern smartphones and operates at a relatively low level of the device’s software stack.
This means that Pixel users must install the latest security update to ensure that the vulnerability has been patched. Google has already released the necessary fix, and security agencies and researchers are monitoring the exploitation of the flaw.